
In this guide
The requested name is part of the checkPreserve the exact trust failureUse a correct supported trust pathHTTPS media delivery depends on establishing an authenticated secure connection. Certificate identity checks help determine whether the presented service identity matches the intended hostname. A certificate error occurs before ordinary media decoding and can prevent later HTTP requests from proceeding.
The error does not mean the video codec is unsupported. It also is not an instruction to turn off verification or replace the hostname with a numeric address.
The requested name is part of the check
Service identity rules compare the intended service reference with certificate identifiers under defined matching procedures. A certificate for one hostname is not a general credential for every host at the same IP address. Aliases, redirects and delivery hosts therefore need correctly configured identity and trust chains.
An original hypothetical playlist loads securely from guide.example but references media.example, whose certificate identity does not match. The first successful HTTPS connection does not certify the second host.
Preserve the exact trust failure
An application can report different failures involving identity, an untrusted issuer, an incomplete chain or other validation conditions. Keep the exact platform message and affected hostname. Android’s troubleshooting guidance treats handshake and certificate-path failures as distinct issues requiring the appropriate certificate/server configuration.
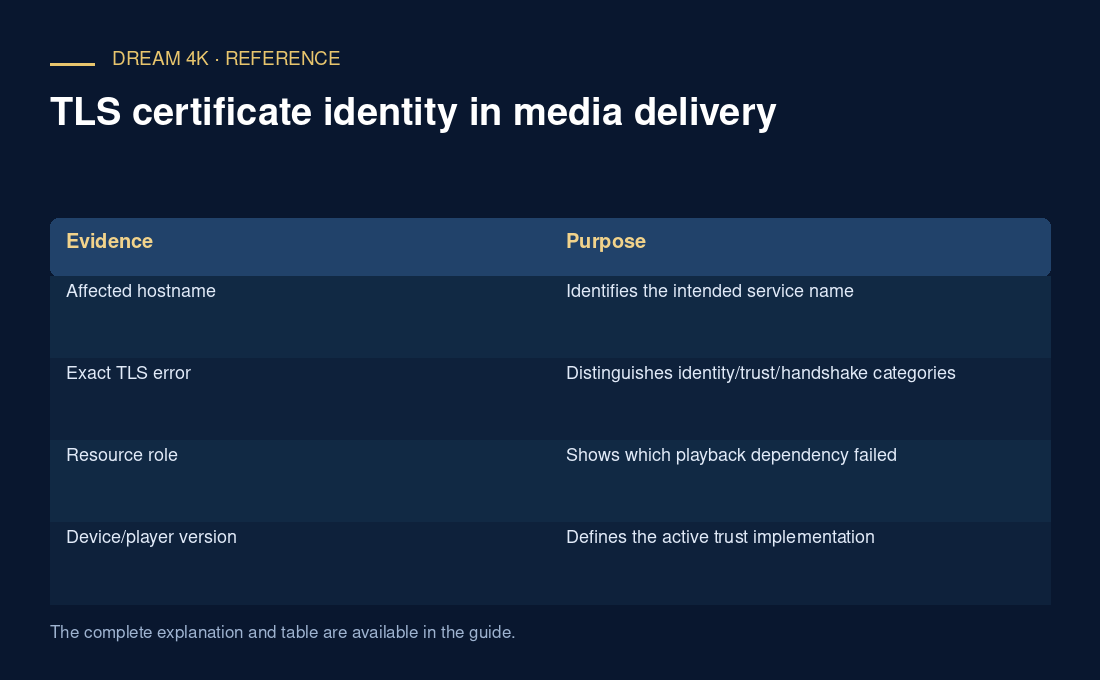
| Evidence | Purpose |
|---|---|
| Affected hostname | Identifies the intended service name |
| Exact TLS error | Distinguishes identity/trust/handshake categories |
| Resource role | Shows which playback dependency failed |
| Device/player version | Defines the active trust implementation |
| Network context | Records managed interception or environment where known |
Use a correct supported trust path
Keep the device and player updated through official channels and follow current platform/source guidance. On a managed network, involve its administrator rather than installing unknown certificates. For source operators, correct the certificate identity and chain on the affected endpoint.
Do not share credentials in a certificate report or accept an unexplained trust exception to make a stream play. A secure failure can be diagnosed from redacted identity and error evidence. Once the connection is valid, HTTP access, media validity and decoder support remain separate checks.