
In this guide
State the known eventName the requested authorityTrack containment separatelyClose with a limited confirmed resultAn escalation should identify what was observed, which account relationship may be affected and what authority is needed next. Keep it factual. A vague label such as hacked can hide whether the issue is a disclosed link, an unfamiliar session or a mistaken local profile.
State the known event
Record the type of information or access involved, where it appeared and the approximate time. Distinguish an actual disclosure from a suspected cause. Do not include the exposed password or token again merely to prove the incident. Use the appropriate private order or case reference.
Name the requested authority
The service provider may need to answer whether credentials can be invalidated. An email provider controls its own session and recovery process. A device manufacturer controls local account removal. Send each question to the party responsible for that relationship.
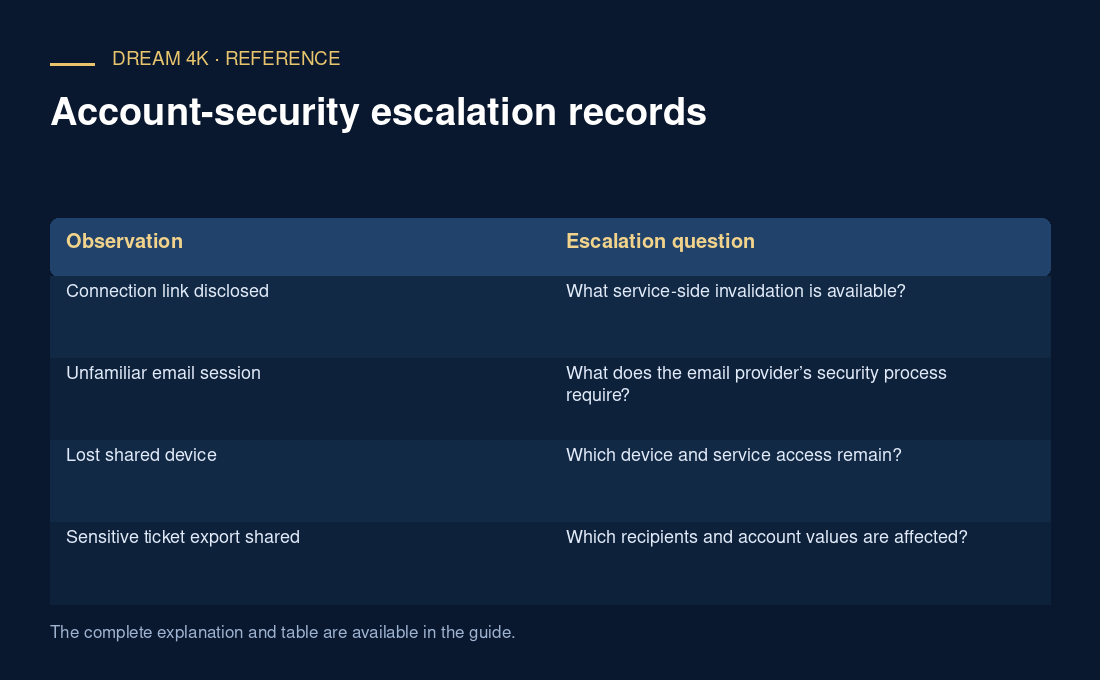
| Observation | Escalation question |
|---|---|
| Connection link disclosed | What service-side invalidation is available? |
| Unfamiliar email session | What does the email provider’s security process require? |
| Lost shared device | Which device and service access remain? |
| Sensitive ticket export shared | Which recipients and account values are affected? |
Track containment separately
Record copy removal, access review and provider-confirmed invalidation as separate events. If an action remains pending, leave it pending. The absence of an error or complaint does not establish that an exposed value was never copied.
Close with a limited confirmed result
Summarise what changed, which authorised devices or records need updating and what remains unresolved. Preserve necessary evidence under appropriate access. Follow actual organisational and applicable reporting obligations where relevant; this guide does not determine legal notification requirements or declare a breach outcome.
Questions about this guide
Should every account error be treated as a security incident?
No. Record the actual evidence. An input error or old profile can have a routine explanation. Escalate security concerns when the observation warrants it, while keeping hypotheses labelled and following the responsible provider’s process.